Home › Security Architecture & Engineering
Graham-Denning Model Explained — Security Models (Part 6)
Security Architecture & EngineeringCISSP
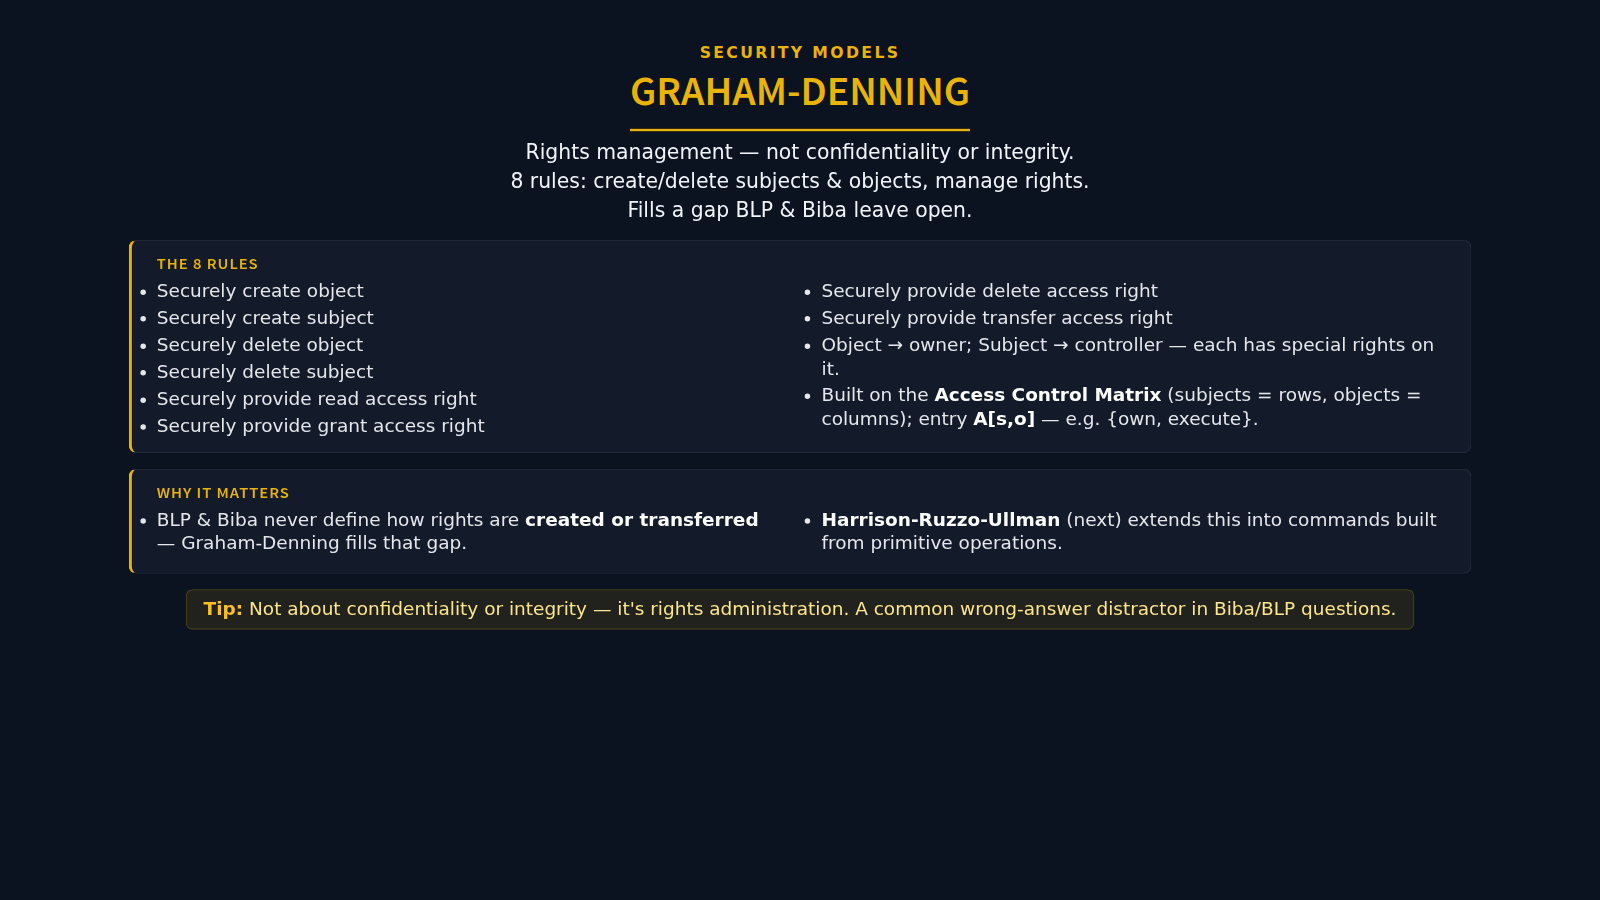
Graham-Denning is different from every model covered so far in this series — it's not about confidentiality or integrity, it's about how access rights themselves get created, assigned, and transferred. In Part 6, we walk through its eight rules and the administrative gap it fills that Bell-LaPadula and Biba leave open.
What you will learn
- What the Graham-Denning model is and why it's not a confidentiality or integrity model
- The eight rules governing subject/object creation, deletion, and rights transfer
- Why Bell-LaPadula and Biba both depend on a gap this model fills
- How Graham-Denning shows up as an exam distractor
- A note on how thin this model's coverage is across CISSP reference material