Home › Communication & Network Security
Identity-Aware Security Explained — Communication & Network Security
Communication & Network SecurityCISSPSecurity+CySA+
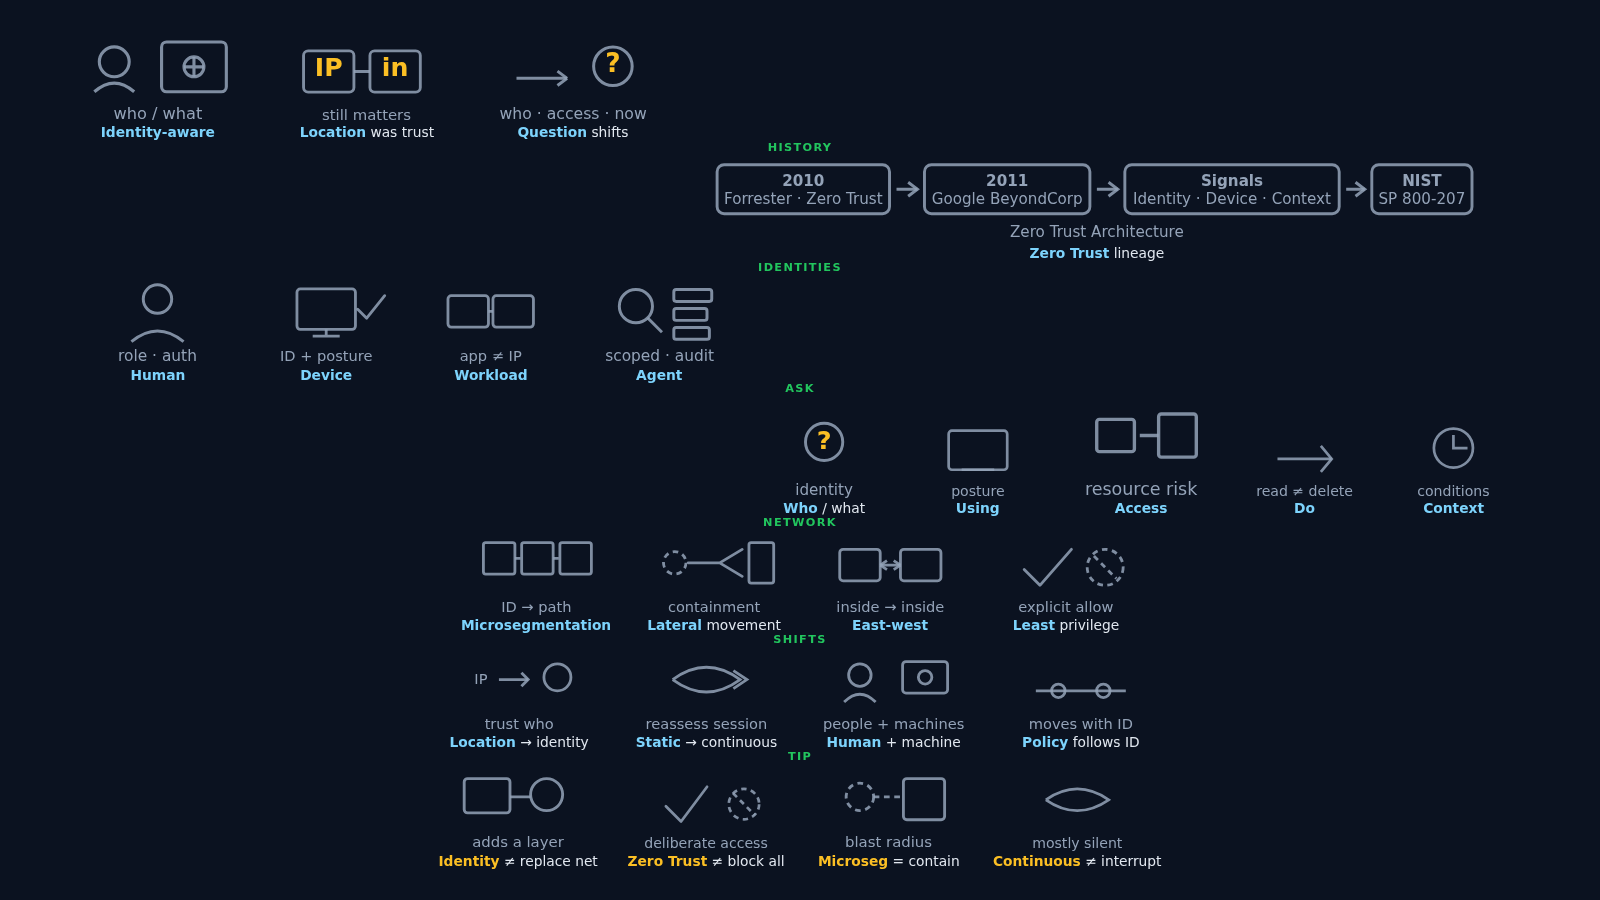
Identity-aware security asks who or what is making a request — not only where the connection came from. In this Communication & Network Security video, we connect the idea to Zero Trust history (Forrester, BeyondCorp, NIST SP 800-207), walk through human, device, workload, and AI-agent identity, five decision questions, continuous access, microsegmentation, and why policy should follow identity.
What you will learn
- Why location-based trust is no longer enough
- Zero Trust lineage: Forrester 2010 → BeyondCorp → NIST SP 800-207
- Human, device (identity vs posture), workload, and agent identity
- Five questions: who/what, using, access, do, context
- Continuous access — authentication once is not always enough
- Microsegmentation, lateral movement, and east-west traffic
- Three shifts: location → identity, static → continuous, human + machine
- Four tip limits: identity, Zero Trust, containment, continuous