Home › Security Assessment & Testing
SOC 1 vs SOC 2 vs SOC 3 Explained: Type I vs Type II Reports
Security Assessment & TestingCISSPSecurity+
How can you trust a vendor's security without auditing the vendor yourself? In this video, I'll walk through SOC reports: who writes them and for whom, the difference between SOC 1, SOC 2 and SOC 3, Type I vs Type II, the Trust Services Criteria, and three common misunderstandings.
What you will learn
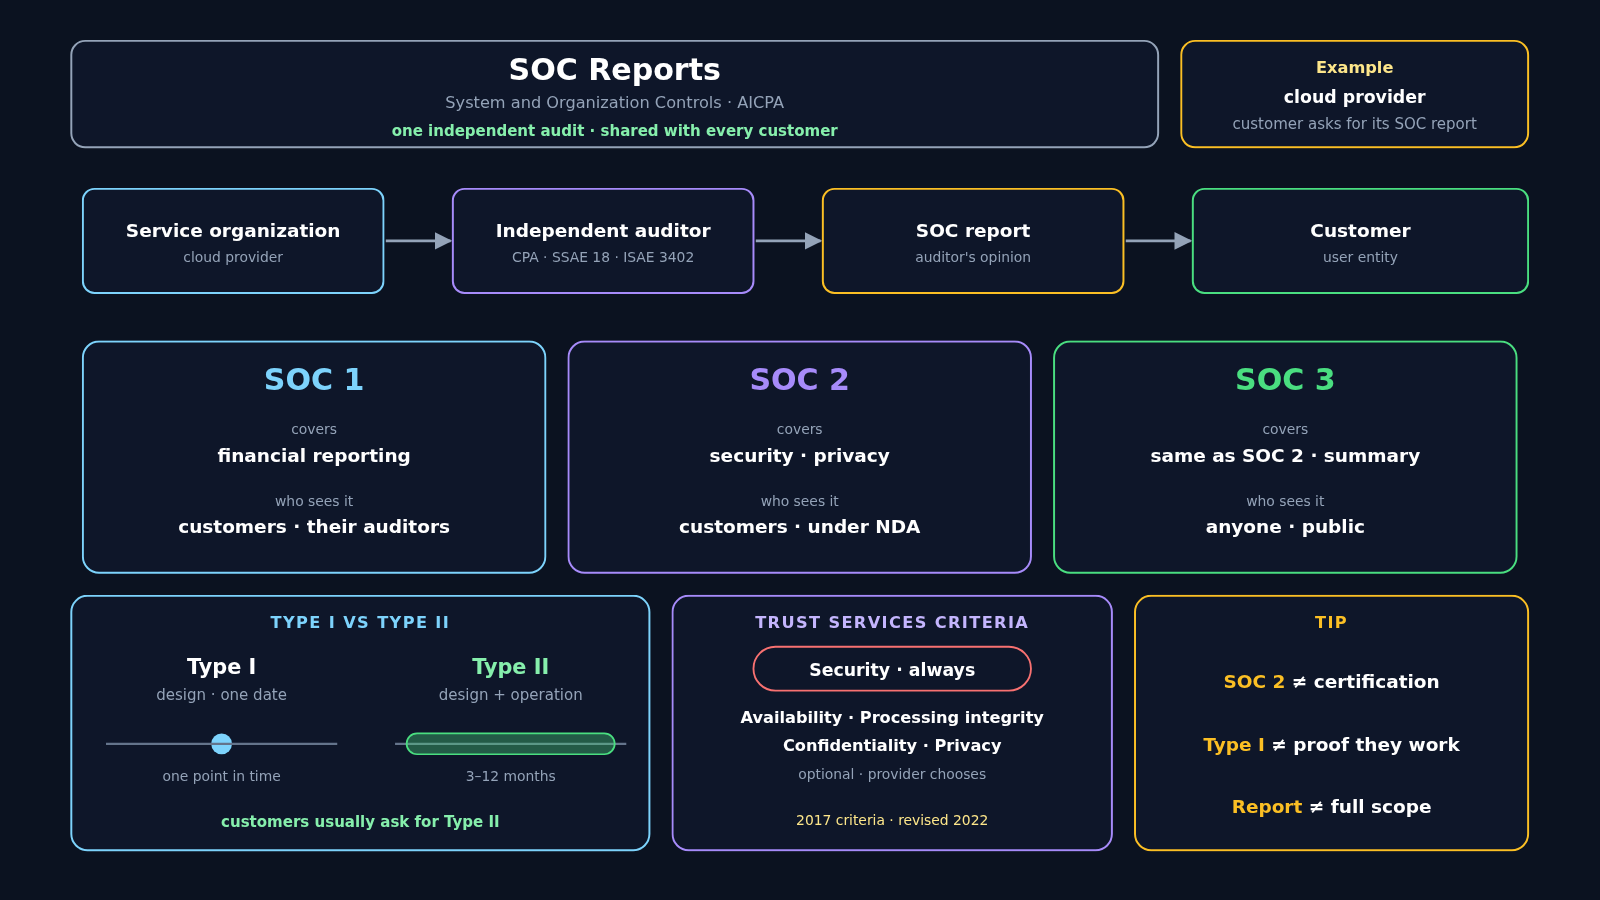
- What System and Organization Controls (SOC) reports are, with a cloud provider example
- The parties: service organization, independent CPA auditor (SSAE 18, ISAE 3402) and the customer
- SOC 1 vs SOC 2 vs SOC 3: what each covers and who sees it
- Type I vs Type II: one point in time vs a period of 3 to 12 months
- The Trust Services Criteria: security always, plus four optional criteria
- Three tip ideas: SOC 2 ≠ certification; Type I ≠ proof they work; report ≠ full scope