Home › Software Development Security
OWASP Agent Control Standard Explained
Software Development SecurityCISSP
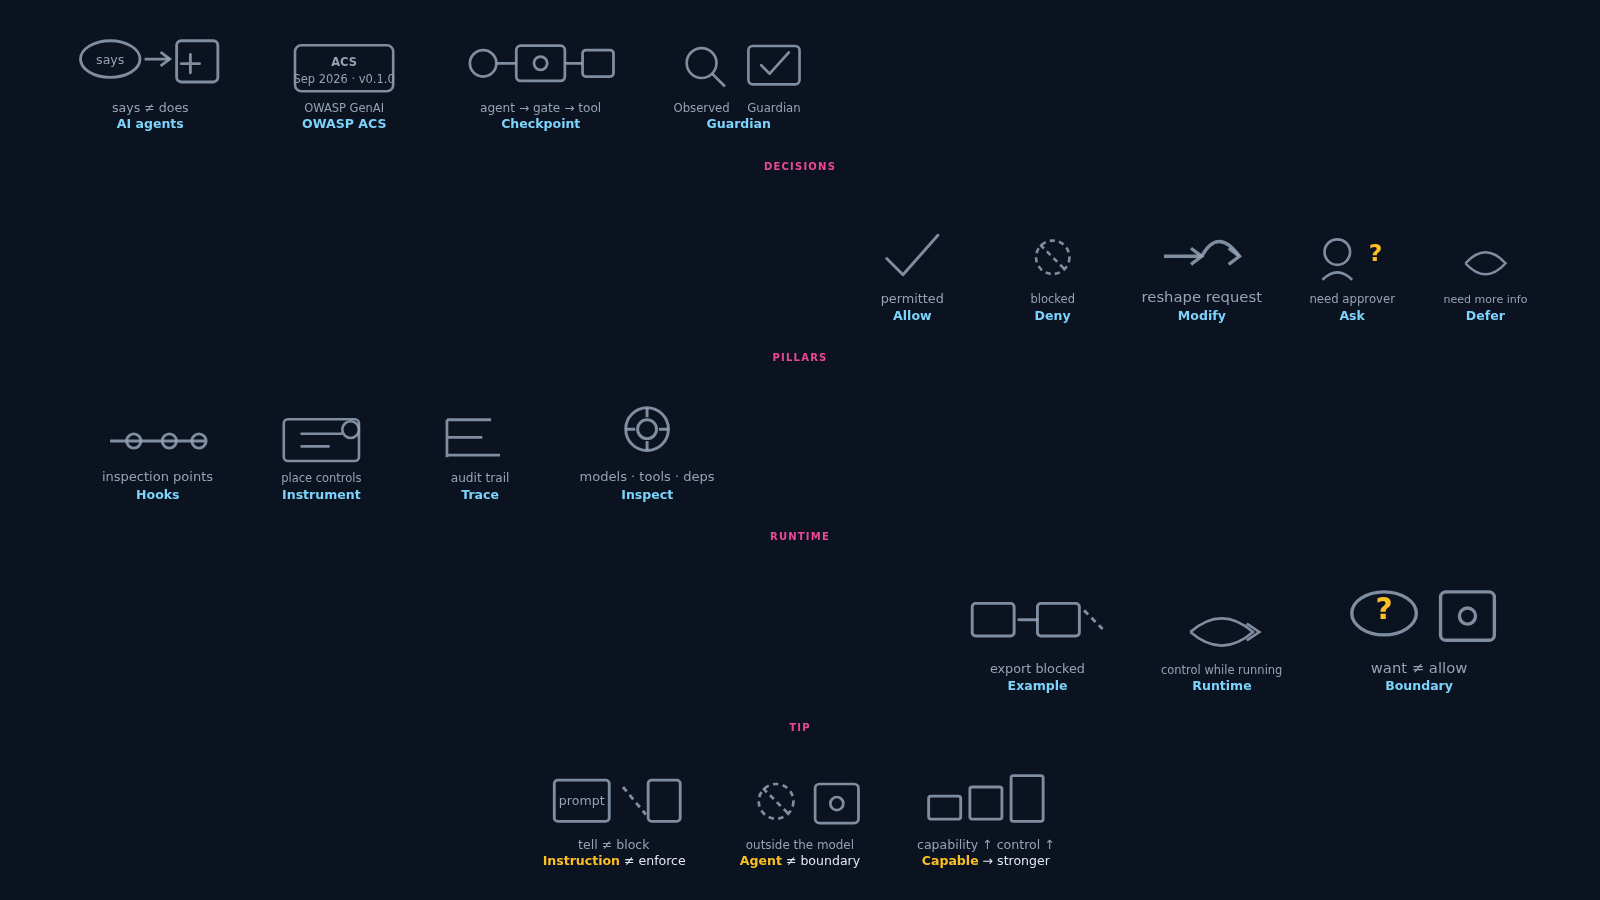
When an AI agent can call tools and change systems, security has to control what it does — not only what it says. In this Software Development Security video I'll explain the OWASP Agent Control Standard (ACS): the checkpoint between agent and action, Guardian vs Observed Agent, five decisions, hooks, Instrument · Trace · Inspect, and why runtime control matters.
What you will learn
- Why agent actions need a security checkpoint
- OWASP ACS (Sep 2026, GenAI Security Project, v0.1.0)
- Observed Agent vs Guardian Agent
- Five dispositions: Allow, Deny, Modify, Ask, Defer
- Hooks and the pillars Instrument, Trace, Inspect
- A runtime example — when export or mass email should be stopped
- Three tip ideas: instruction ≠ enforcement; agent ≠ boundary; capability needs stronger controls