Home › Security & Risk Management
EU Cyber Resilience Act (CRA) Explained
Security & Risk ManagementCISSP
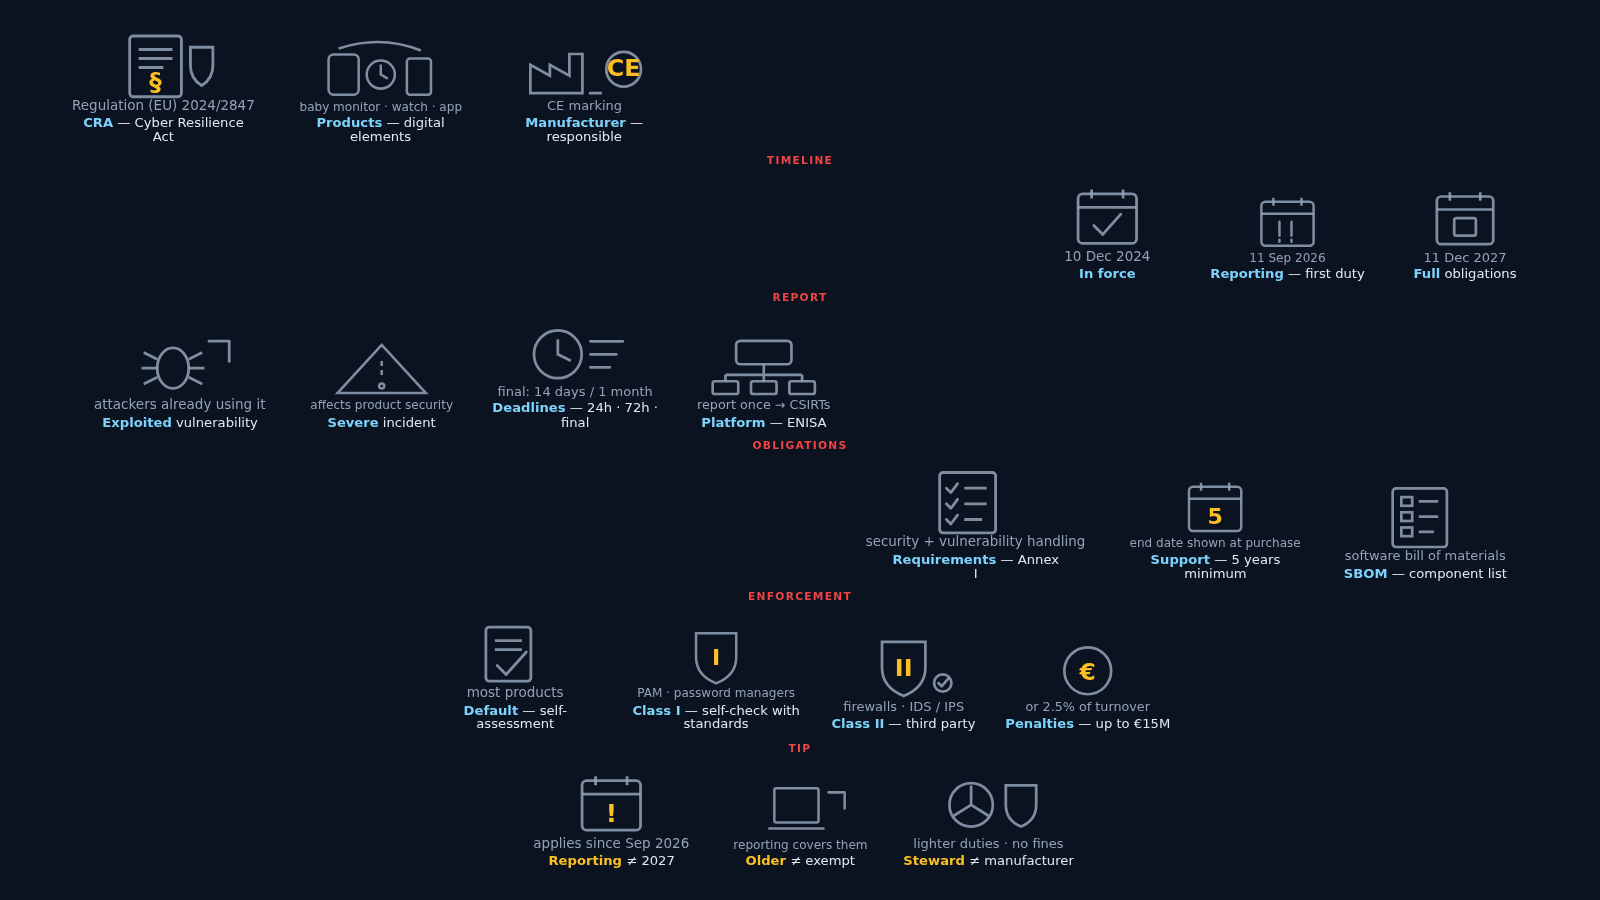
Since 11 September 2026, manufacturers selling connected products in the EU must report actively exploited vulnerabilities within 24 hours. In this video, I'll walk through the EU Cyber Resilience Act (CRA): which products it covers, the three dates that matter, what must be reported and how fast, the duties for the products themselves, how the rules are enforced, and three common misunderstandings.
What you will learn
- What the Cyber Resilience Act is, which products with digital elements it covers, and why the manufacturer is responsible
- The timeline — in force 10 Dec 2024, reporting from 11 Sep 2026, full obligations from 11 Dec 2027
- Reporting — exploited vulnerabilities and severe incidents, the 24h / 72h / final deadlines, and ENISA's Single Reporting Platform
- Product duties — the Annex I requirements, a support period of at least five years, and the SBOM (software bill of materials)
- Enforcement — default, Class I and Class II products, and penalties up to €15 million or 2.5% of turnover
- Three tip ideas: reporting ≠ 2027; older ≠ exempt; steward ≠ manufacturer